Employees now work from anywhere, on corporate or personal devices. Traditional VPNs, which expose an internet-facing gateway and often provide broad network access, have become prime targets: vulnerability exploitation is now the leading initial-access vector in breaches, while tens of thousands of stolen VPN and firewall credentials are circulating.
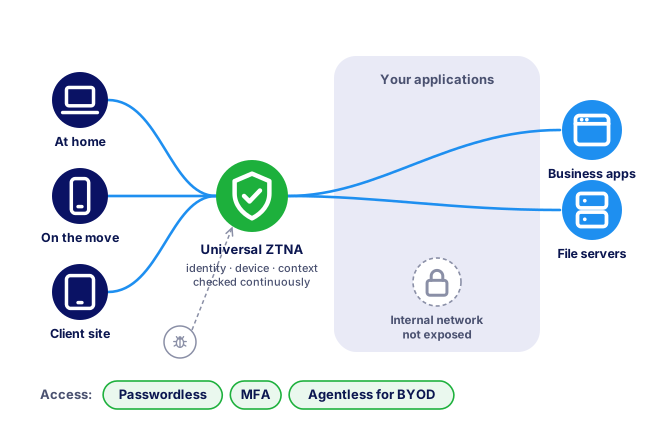
Ekinops takes a Zero Trust approach. Universal ZTNA continuously verifies identity, device health, and context, granting access only to authorized applications, never to the underlying network, with no internet-facing exposure. The same web-filtering policy follows users wherever they connect, ensuring consistent protection. Already trusted by over 500 European organizations, including hospitals, local governments, and public agencies, Ekinops provides a more secure approach to today’s distributed workforce
Securing nomadic users raises three questions most DSI and RSSI teams face early on:
A VPN checks the user once, when the tunnel opens, then places them on the internal network. Ekinops U-ZTNA verifies identity, device, and context on every connection and throughout the session, and only grants access to the specific applications the user is authorized for. Connections are outbound-only, so there is no login portal exposed on the internet for attackers to scan.
Access is cut immediately. If antivirus protection is disabled or out of date, for example, the active tunnel is closed without waiting for the session to end. Access rules can also adapt to IP address, country, and time of connection.
Through the agentless portal: users reach applications from their browser, authenticated via OIDC through your identity provider. It covers HTTP, HTTPS, SSH, and RDP, with session recording for privileged protocols. The external device stays fully isolated from your network core.
In Europe. Universal ZTNA runs on trusted European cloud infrastructure, such as OVHcloud, Outscale, and Scaleway, and can also be deployed in a private cloud or on-premise. Traffic is end-to-end encrypted (AES-256), so the infrastructure operator, Ekinops included, cannot read it.
Yes. U-ZTNA deploys alongside your existing VPN, firewalls, identity provider, and SIEM. You migrate application by application, starting with the most sensitive, and retire the VPN only when you’re ready.