
Every contractor, every subsidiary, every remote hire adds another set of credentials that can end up reaching more than it should. Zero Trust access closes that gap by design: each user only reaches the specific applications they’re cleared up for, not the network behind them. Every connection is verified and encrypted, whether someone is logging in from headquarters, a partner site, or their kitchen table, whatever device is used (PCs, mobiles phones, tablets, etc.).
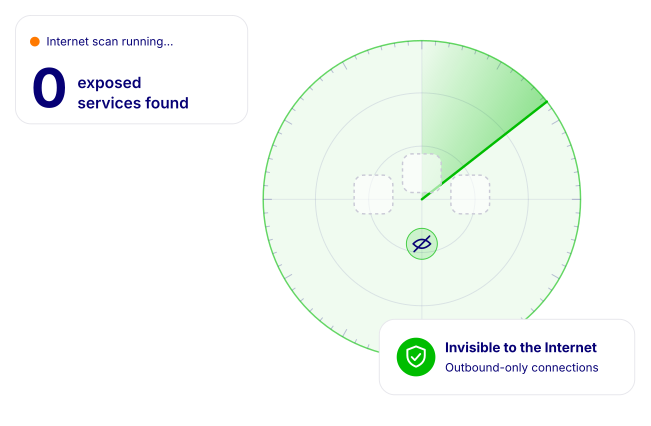
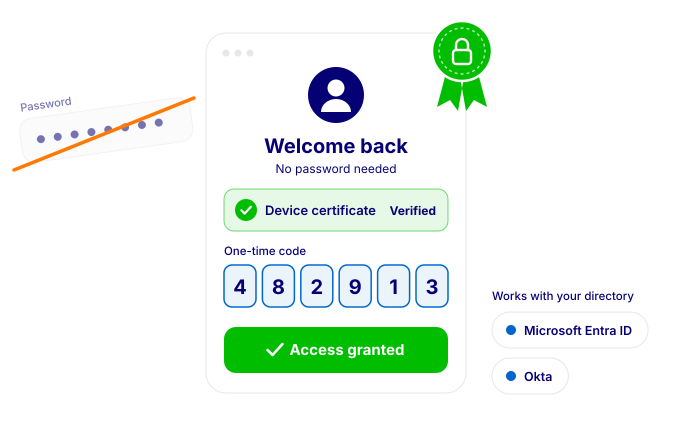
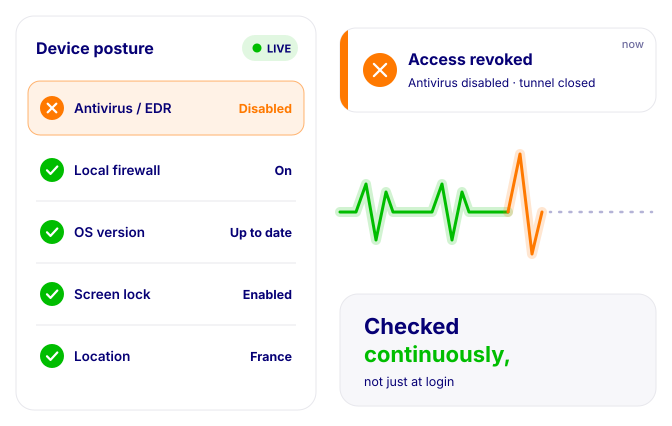
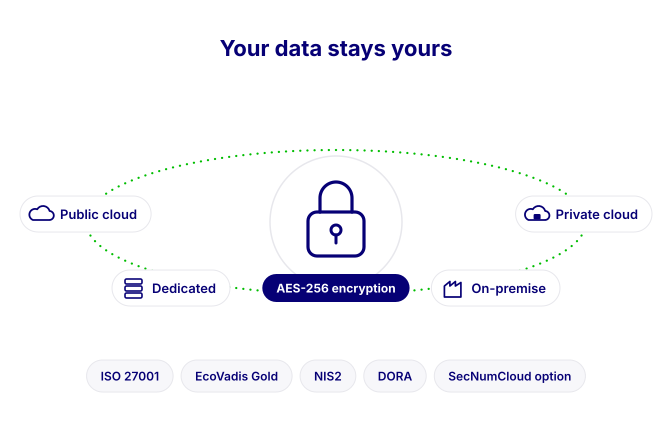
Ekinops U-ZTNA never exposes neither your applications nor your infrastructure; and never asks you to trust a third party, not even Ekinops. Traffic is end-to-end encrypted and routed by cryptographic keys, and the whole solution can run as a service, on-premises or hybrid, operated by you or your MSSP.
A zero-exposure access solution: your applications become invisible on the internet and accessible only to verified users, application by application, never the whole network.
One access model for web, client-server, SSH/RDP, containers and clouds, 5 000+ protocols, regardless of user location (local network or mobile). This is the “universality” criterion.
Yes. Universal ZTNA runs on trusted European cloud infrastructure, such as OVHcloud, Outscale, and Scaleway, and is designed to meet GDPR requirements.
Your team. Users, applications, and access rules are all managed from the same centralized console, so IT keeps full control without depending on us for routine changes.
Yes. U-ZTNA deploys standalone, alongside existing firewalls, VPN, IdP (Entra ID, Okta) and SIEM/SOC. App-by-app, reversible migration — no rip-and-replace, no platform lock-in.