


Upgrade your branch network to SD-WAN without replacing a single router
Why implement SD-WAN?
Every new site or office used to mean weeks of waiting for network changes, backup links to negotiate, and a growing list of appliances to manage remotely. Meanwhile, your teams already live in SaaS applications like Microsoft 365, and routing that traffic through a central data center just adds delay for no real benefit. Ekinops SD-WAN (Software-Defined Wide Area Network) gives you one network that adapts automatically, keeps sites online when a connection drops, and lets your SaaS apps take the fastest path, without adding new hardware or a specialist at every branch.
-
Growing Without Growing Your IT Team
Open a new site and get it connected and secured the same week, not the same quarter, without sending an engineer on-site. -
Faster Apps, Lower Cost
Let everyday SaaS Apps like Microsoft 365 reach the internet directly from each branch, instead of slowing down and adding cost to your private network. -
Never Lose a Sale to a Dropped Connection
If one internet or MPLS line fails, your business keeps running: traffic switches to a working line in under 3 seconds, with nobody noticing.
What this brings to your network


What's inside Ekinops SD-WAN
ANALYTICS
CLOUD BREAK-OUT
NETWORK FIREWALL
MULTI-SITE NETWORK
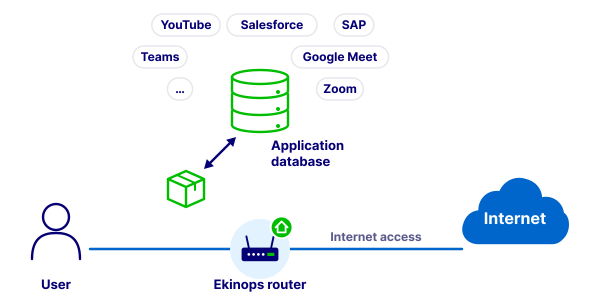
See and prioritize every application from the first packet
- Identifies more than 7,000 applications and SaaS services from the very first network packet, for instant routing and prioritization decisions.
- Gives full visibility into bandwidth consumption by application and by site from a central dashboard, surfacing unauthorized shadow IT services.
- Monitors latency, jitter, and packet loss in real time to speed up troubleshooting and anticipate bandwidth needs.
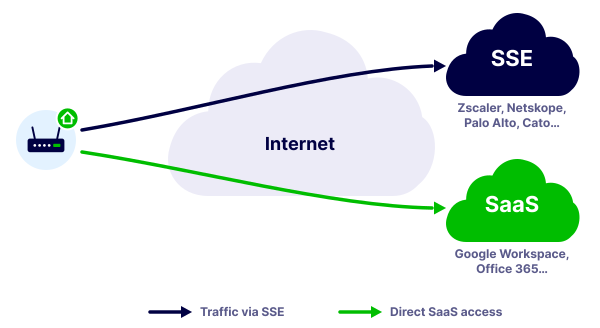
Send trusted traffic straight to the cloud, not through a central hub
- Routes approved SaaS traffic, such as Microsoft 365 or Salesforce, directly to the internet from the branch instead of backhauling it through a central hub.
- Frees up capacity on private interconnection links by keeping trusted cloud traffic off them entirely.
- Automatically and securely redirects other branch internet traffic to leading cloud security gateways, such as Ekinops SSE, Zscaler, Palo Alto Prisma, or Cato Networks, for filtering at scale.
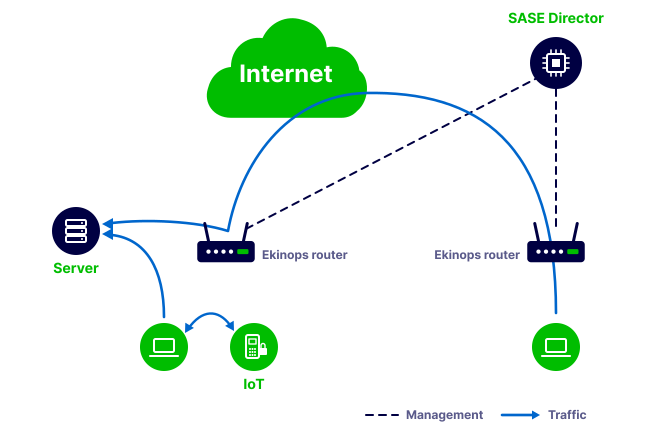
Stateful security built into every branch router
- Runs stateful TCP/UDP inspection with security profiles by zone, event logging, and malicious IP detection.
- Applies granular access control rules based on source and destination IP, protocol, port range, and traffic priority (TOS/DSCP).
- Perform SaaS application filtering (7000+) to prevent Shadow IT
- Define your log policies per rules, investigate or export those logs to a SIEM
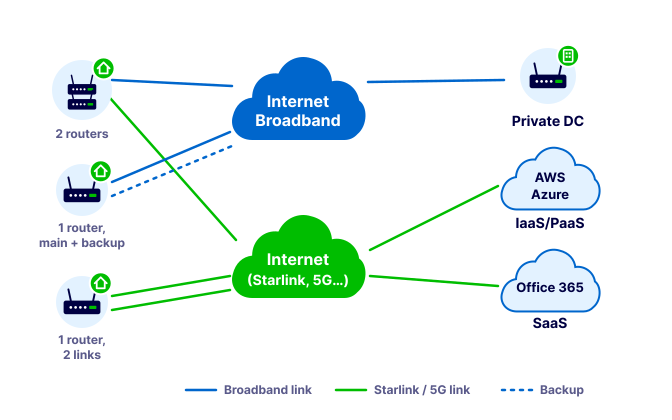
Combine every WAN link into one resilient network
- Manages multiple underlay links (MPLS, fiber, 4G/5G, satellite) simultaneously, in active/active, active/passive, or backup mode.
- Deploys encrypted overlay topologies automatically in hub-and-spoke mode.
- Segments remote sites into isolated logical groups, blocking direct network-to-network routing between them for confidentiality.

They build secure, resilient networks with Ekinops
-
“The solution we delivered to VGRD is perfectly seamless, easy-to-operate and to deploy. Now, all ecotel customers can benefit from additional OneOS6 features, such as containers support, Firewall or SD-WAN, without any additional hardware deployment.”
Markus HendrichChief Executive Officer at ecotel
-
“Rising traffic pressure combined with technological evolutions posed several critical challenges for our network. Ekinops worked closely with us to define a solution that can optimize network performance as well as secure business applications access within the legal framework in which we operate.”
Christophe Orieulx de la PorteChief Technology Officer at ADNOV
How does licensing work? Am I paying for capacity I'm not using?
No. Licensing is consumption-based: routing, security, and SD-WAN features activate in software as you turn them on, so you pay for the capacity and functions you actually use, and add more later without swapping hardware.
What's the difference between the SD-WAN tiers you offer?
SD-WAN is built for SMBs, franchise networks, and small branch or point-of-sale sites: a simplified, one-box approach to hybrid WAN and local internet breakout at a competitive price. Secure Connect targets customers willing to have a better experience with their Internet connectivity without the need to interconnect their sites (multi-site network). Both run on the same hardware and orchestration platform, so you can start with one and move to the other without a re-architecture. You also have options in deployment model (SaaS) and Ekinops also have dedicated models for Channel.
How does this scale for service providers managing thousands of customer sites?
SD-WAN Director, our central orchestration platform, manages up to 30,000 CPE devices per active instance, with a three-tier role-based structure (service provider, partner, customer) and self-service portals at every level, so operators can delegate specific configuration or security tasks to their customers while keeping the underlay under their own control.
Am I locked into proprietary hardware and protocols?
No. The encrypted overlay relies on open, standard protocols, dynamic virtual tunnel interfaces to establish site-to-site links on demand, with IKEv2 encryption and BGP route propagation, rather than a closed, proprietary tunneling scheme. If you don’t want to deploy a physical router, our virtual router can also run as a VM or container on any standard hypervisor or uCPE server, including third-party white boxes.
Do I need to keep my MPLS lines, or can I run this over internet connections only?
Either. SD-WAN manages whichever underlay links you have, MPLS, fiber, 4G/5G, or a mix, so you can keep MPLS where you need its guarantees and add cheaper broadband or cellular elsewhere, with traffic routed intelligently across all of them.